Control systems | PLC cybersecurity
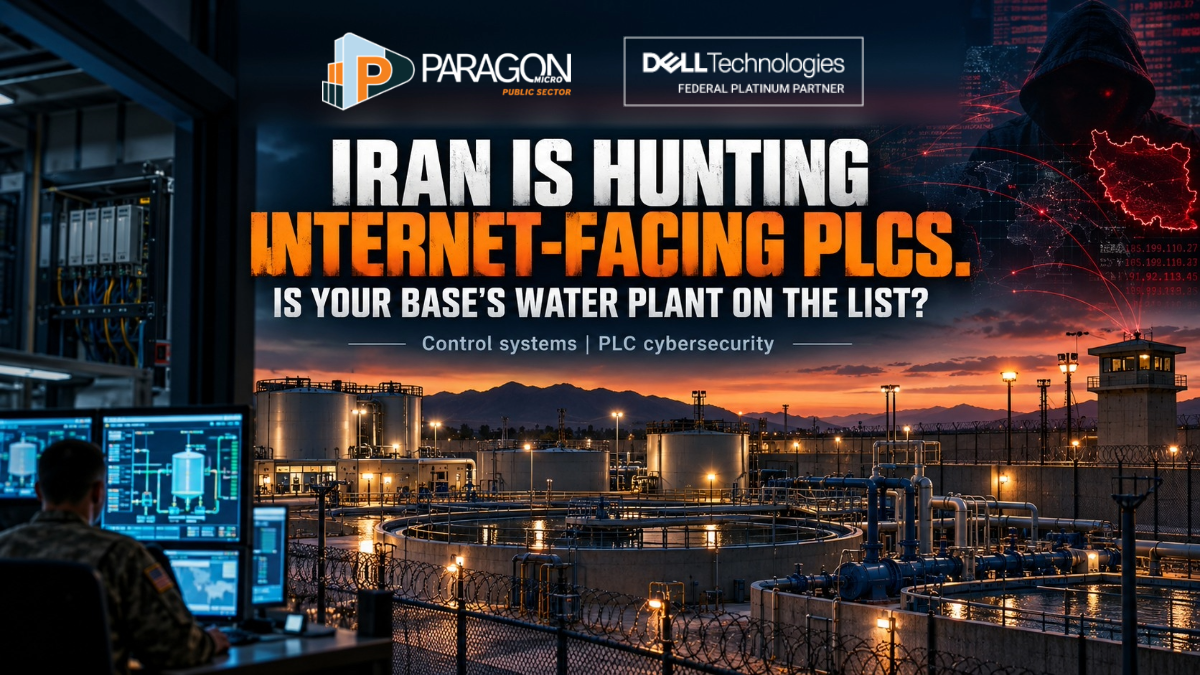
Actors affiliated with Iran are hunting internet-facing controllers. Find yours before they do.
On April 7, 2026, U.S. agencies warned that actors affiliated with Iran were exploiting internet-facing PLCs, the small controllers that run industrial equipment, in water, energy, and local government systems. A July update added more brands and newer techniques. Base water, power, building controls, and access control run on the same kinds of controllers. Here is how to take them off the internet and keep them off.
01 | The advisory
What the April advisory and its July update said
On April 7, 2026, the FBI, CISA, NSA, EPA, the Department of Energy, and U.S. Cyber Command's Cyber National Mission Force warned that actors affiliated with Iran were exploiting internet-facing programmable logic controllers across U.S. critical infrastructure.
The advisory, AA26-097A, named Rockwell Automation and Allen-Bradley CompactLogix and Micro850 controllers, and said other brands, including Siemens S7, may also be targeted. The victims were in government services and facilities, including local municipalities, water and wastewater systems, and energy.
The actors used overseas IP addresses and leased third party hosting to reach controllers exposed to the internet, then used the vendor's own configuration software to make a connection the controller accepted. They "maliciously interacted with project files and altered data displayed on HMI and SCADA displays," and the activity caused "operational disruption and financial loss" in some cases.
The July update widened it
More brands
Schneider Electric and Siemens
The update added Schneider Electric BMX P34 and Modicon M340 and Siemens S7-1200 controllers to the Rockwell devices, and said other brands may be targeted.
More paths in
Cellular modems
It covered cellular modems that connect controllers, including 1 case of an SSH server running on port 22.
More damage
Disabled safety logic
Its description of data manipulation now covers changes to reusable logic blocks and disabled shutdown and alarm logic.
More agencies
7 coauthors
The Department of the Treasury joined the original 6 agencies and commands on the update, dated July 22, 2026.
A similar campaign hit U.S. water systems in 2023. In a December 2023 advisory, the FBI, CISA, NSA, EPA, and Israel's National Cyber Directorate said that beginning on November 22, 2023, actors affiliated with the IRGC accessed multiple U.S. water facilities through Unitronics controllers "publicly exposed to the internet with default passwords."
This article takes no position on the war. It covers a defensive control that applies to any base, whoever is scanning.
The question for your base
Could someone outside the fence reach any controller that runs your water, power, or gates?
If nobody on the base can answer that today, the advisory says start there.
02 | The base
A base runs on the same controllers the advisory names.
UFC 4-010-06, the Unified Facilities Criteria for cybersecurity of facility related control systems (dated October 10, 2023), lists what those systems include: "building control systems, utility control systems, electronic security systems, and fire and life safety systems." Those are a base's water and wastewater plants, power distribution and generators, heating and cooling, gates, cameras, and alarms.
The criteria already point the same direction as the advisory. Section 4-1.1 says to "Avoid dependence on the network for the execution of control strategies," and "When dependence on the network is unavoidable, isolate that portion of the network as much as possible." Section 4-4 is titled "Do Not Provide Remote Access."
The department's zero trust guidance for operational technology, posted in November 2025, sets 105 activities for systems like these, with 84 at target level and 21 at advanced level. FORTRESS America makes installation hardening and cyber resilience 1 of its 5 pillars. An internet-facing controller on a base works against all 3.
03 | The steps
PLC cybersecurity on a base, step by step
These steps come from the 2026 advisory and its update, applied to the systems a base runs.
| Step | What to do | Why |
|---|---|---|
| 1. Find them | Inventory every controller, operator screen, and cellular modem on water, power, building, and security systems, and check which can be reached from the internet | The actors found their targets by scanning for internet-facing devices |
| 2. Take them off the internet | Disconnect each controller from the public internet, and broker any remote access through a secure gateway or jump host | The advisory's first immediate step, and UFC 4-010-06 says not to provide remote access |
| 3. Restrict who can talk to them | Set firewall rules or access lists so only authorized control system devices reach each controller, and block hosting provider addresses | The actors connected from leased third party hosting |
| 4. Close the cellular side door | Use private cellular networks, zero trust network access, or site to site VPNs for any controller on a cellular modem | The update covers cellular modems, including 1 with an SSH server exposed |
| 5. Lock the controller | Keep the physical mode switch in run, turn on programming protection, and replace every default password | The 2023 campaign succeeded through default passwords |
| 6. Know the good logic | Keep known good copies of each controller's logic offline, compare running logic against them, and verify backups before restoring | The update describes disabled shutdown and alarm logic |
| 7. Tell your integrators | Make sure every contractor and service provider with access to these systems knows about the active threat | The update calls this out directly |
Our rule of thumb
A controller should be reachable only by the devices that run it. Any other path to it is a path for someone else.
04 | Separation
Separate the control networks from everything else on base.
Taking controllers off the internet closes the front door. Separating the control networks from the rest of the base network closes the side doors: a compromised office laptop or camera should not be able to reach the controller that runs the water plant.
In practice that means each control system sits on its own network segment, the only traffic allowed in or out is traffic the system needs, and every crossing point is logged. It also means a recovery plan with offline copies of controller logic and configurations, so a tampered controller can be restored to a known good state. Chapter 10 of our Dell Federal guide covers that recovery side.
05 | How we help
Where Dell Federal and Paragon Micro fit
As a Dell Technologies Federal Platinum Partner and multi-vendor technology provider, we design the network segmentation, access control, and recovery that keep a base's control systems off the internet and apart from the rest of the network.
Segmentation
Networks that limit lateral movement
We design zero trust architecture around users, devices, applications, and data flows, including network segmentation, and support authority to operate documentation through the authorization process.
Access
Identity and access control
We design identity and access control that includes multifactor authentication, role based access, and device trust checks, for the people and systems that touch control networks.
Past performance
Keesler Air Force Base
We modernized the base's video surveillance system: 732 IP cameras covering the entry gates, flight line, Base Defense Operations Center, and Command Post, taken through the DoWIN Approved Products List process and delivered with as built diagrams.
Built before it ships
The System Readiness Center
In our 55,000 plus square foot secure facility, we validate configurations and stage and test systems before they reach the installation.
From order to support
If your team doesn't have the people to separate the control networks from the base network, we can do that work with you.
- 01
We sell it
The firewalls, switches, and servers that split each control network from the base network and host the remote access gateway
- 02
We install and integrate it
Staged and tested in our System Readiness Center, then installed on base and connected to the networks your control systems use today
- 03
We train your team
Your operators and network staff learn the new access rules and how to reach a controller through the gateway
- 04
We support it after
Lifecycle sustainment, current configuration records, and upgrade planning after delivery
Paragon Micro | Dell Federal
Take your controllers off the internet.
Send us the control systems on your installation and how each one connects today. We can help design the segmentation, the secure gateway for remote access, and the offline recovery copies, then stage and test them before they go live.
Army organizations and other federal agencies can order through ITES-4H. The Missile Defense Agency and other Department of War organizations can order through MDA SHIELD, and federal buyers can also use GSA. The right path depends on scope, eligibility, and ordering rules.
Keep reading
FORTRESS America: installation IT that stays up
Chapter 15 of our Dell Federal guide covers the base as a control system network, chapter 18 covers the control system criteria, and our FORTRESS America article covers installation IT and security.
Answers for installation teams
PLC cybersecurity: common questions
What is PLC cybersecurity?
It is the protection of programmable logic controllers, the small computers that run pumps, valves, generators, and other industrial equipment, from unauthorized access and tampering. The core steps are keeping controllers off the internet, limiting who can reach them, locking their configuration, and keeping known good copies of their logic.
What did the April 2026 advisory warn about?
Advisory AA26-097A, from the FBI, CISA, NSA, EPA, the Department of Energy, and U.S. Cyber Command's Cyber National Mission Force, warned that actors affiliated with Iran were exploiting internet-facing PLCs in water, energy, and government facilities, altering what operator screens displayed and in some cases causing operational disruption and financial loss.
Which PLCs are affected?
The April advisory named Rockwell Automation and Allen-Bradley CompactLogix and Micro850 controllers. The July 22 update added Schneider Electric BMX P34 and Modicon M340 and Siemens S7-1200 controllers, and said other brands may be targeted.
Do military bases run these kinds of controllers?
Yes. UFC 4-010-06 defines facility related control systems to include building control systems, utility control systems, electronic security systems, and fire and life safety systems, which covers a base's water, power, heating and cooling, gates, and alarms.
What is the first thing to do?
Find every controller that can be reached from the internet and disconnect it from the public internet, with any remote access brokered through a secure gateway or jump host. That is the first immediate step in the advisory.
How does Paragon Micro help?
We design network segmentation, identity and access control, and recovery for control systems, support authority to operate documentation, and stage and test systems in our System Readiness Center. At Keesler Air Force Base, we modernized a 732 camera security system and took it through the DoWIN Approved Products List process.
Reference desk
Sources and further reading
Public sources as reviewed October 22, 2026. Advisories are updated as investigations continue, so check the current version before you act on it.
ViewHide 13 sourcesPrimary and supporting references
Department of Defense. (2023, October 10). Cybersecurity of facility-related control systems (UFC 4-010-06). Whole Building Design Guide. https://www.wbdg.org/FFC/DOD/UFC/ufc_4_010_06_2023.pdf
Easley, M. (2025, December 1). Pentagon posts guidance on implementing zero trust for operational technology. DefenseScoop. https://defensescoop.com/2025/12/01/dod-guidance-implementing-zero-trust-for-operational-technology-ot/
Federal Bureau of Investigation, Cybersecurity and Infrastructure Security Agency, National Security Agency, Environmental Protection Agency, & Israel National Cyber Directorate. (2023, December 1; updated 2023, December 14). IRGC-affiliated cyber actors exploit PLCs in multiple sectors, including U.S. water and wastewater systems facilities (AA23-335A). https://media.defense.gov/2023/Dec/04/2003350920/-1/-1/0/CSA-IRGC-AFFILIATED-CYBER-ACTORS-EXPLOIT-PLCS-IN-MULTIPLE-SECTORS.PDF
Federal Bureau of Investigation, Cybersecurity and Infrastructure Security Agency, National Security Agency, Environmental Protection Agency, Department of Energy, & U.S. Cyber Command Cyber National Mission Force. (2026a, April 7). Iranian-affiliated cyber actors exploit programmable logic controllers across US critical infrastructure (AA26-097A). https://www.ic3.gov/CSA/2026/260407.pdf
Federal Bureau of Investigation, Cybersecurity and Infrastructure Security Agency, National Security Agency, Environmental Protection Agency, Department of Energy, U.S. Cyber Command Cyber National Mission Force, & Department of the Treasury. (2026b, July 22). Iranian-affiliated cyber actors exploit programmable logic controllers across US critical infrastructure (AA26-097A, updated). https://www.ic3.gov/CSA/2026/260722.pdf
Paragon Micro. (n.d.-a). Dell Federal. https://www.paragonmicro.us/partners/dell-federal/
Paragon Micro. (n.d.-b). Keesler Air Force Base video surveillance modernization. https://www.paragonmicro.us/past-performance/keesler-air-force-base-video-surveillance-modernization/
Paragon Micro. (n.d.-c). Secure integration & staging facility. https://www.paragonmicro.us/about-us/facility/
Paragon Micro. (n.d.-d). Video surveillance & physical security. https://www.paragonmicro.us/solutions/video-surveillance-and-physical-security/
Paragon Micro. (n.d.-e). Zero trust & cyber resilience for government. https://www.paragonmicro.us/solutions/zero-trust-and-cyber-resilience/
Paragon Micro. (2026a). Dell Federal and Paragon Micro: How the partnership is positioned for FORTRESS America, Project Meridian, and the Autonomous Warfare Command. https://www.paragonmicro.us/dell-federal-paragon-micro-dow-initiatives/
Paragon Micro. (2026b, October 2). FORTRESS America: What independent bases need from their IT and security systems. https://www.paragonmicro.us/fortress-america-installation-it-security/
Whittaker, Z. (2026, April 7). Iranian hackers are targeting American critical infrastructure, US agencies warn. TechCrunch. https://techcrunch.com/2026/04/07/iranian-hackers-are-targeting-american-critical-infrastructure-u-s-agencies-warn/